
Muin for Compliance: Framework Management, Risk Registers, and Audit Readiness
A comprehensive guide to using Muin's Compliance module for regulatory framework tracking, gap analysis, risk assessment, and audit management.

Names and scenarios in this article are illustrative, not real customer stories. They represent common patterns we hear from compliance teams at growing businesses.
Compliance isn’t optional, and for most organizations it often feels impossible. You need to track regulatory frameworks, maintain evidence, conduct risk assessments, and prepare for audits, usually with fewer people than the work calls for. That holds at a 40-person startup and at a 1,500-person company whose compliance team covers several frameworks.
The typical approach is spreadsheets. A SOC 2 readiness tracker here, a HIPAA checklist there, a folder of screenshots somewhere else. It works until it doesn’t: an auditor asks for evidence you can’t find, a framework updates and nobody notices, or a critical control gap goes undetected.
The numbers make the case clear: in the most recent multi-industry study on this question, Ponemon Institute research published in 2017, the average cost of compliance was $5.47 million, while the cost of non-compliance averaged $14.82 million, 2.71 times higher. Regulatory enforcement and penalty exposure have only increased since then (GDPR entered force in 2018, state privacy laws have proliferated, and SEC cybersecurity disclosure rules tightened in 2023–24). For any organization, a single audit failure or regulatory fine is costly. For a smaller one, it can threaten the business itself.
Muin for Compliance changes the equation by bringing enterprise-grade compliance management to teams of any size.
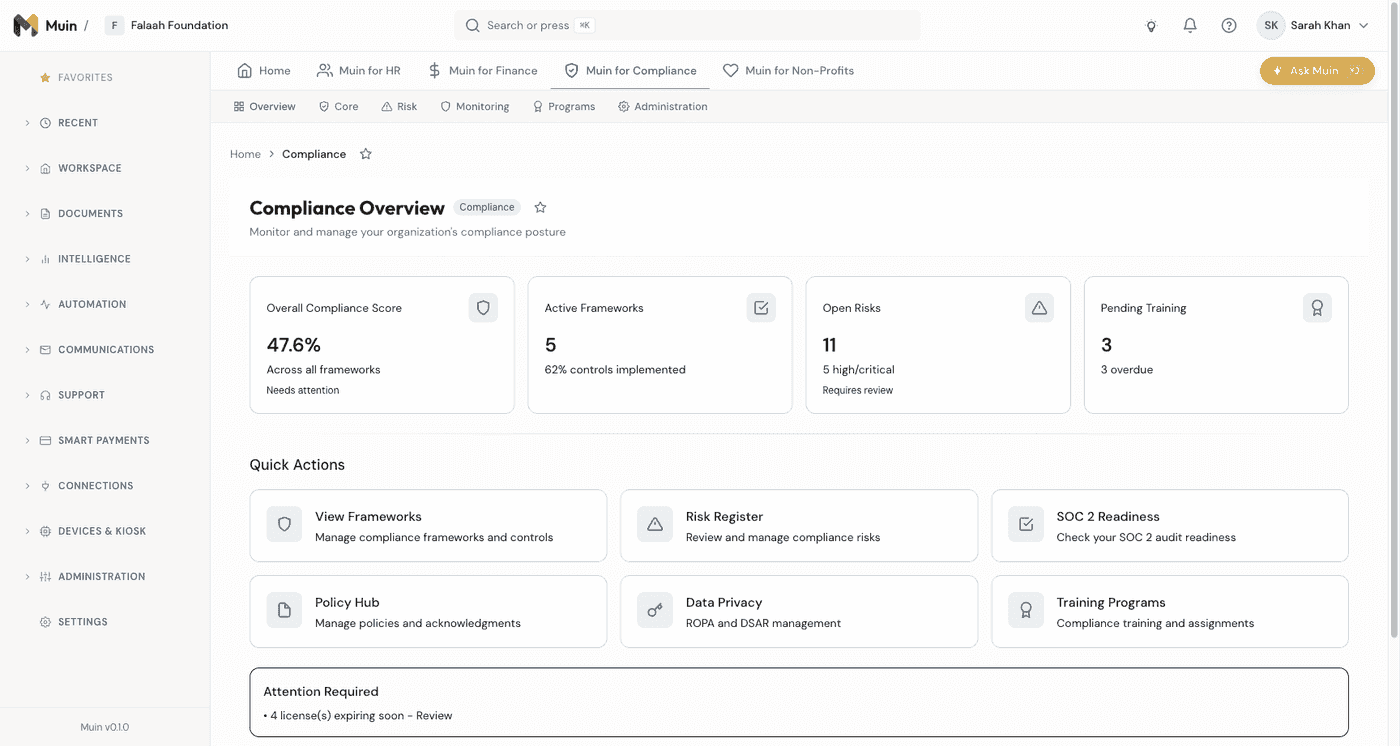
Priya was hired to build a compliance program from scratch at a 40-person fintech startup. She inherited a shared drive full of unlabeled policy documents and a SOC 2 audit scheduled for four months out. In her first week, she ran Muin’s compliance scanner and found 12 policy gaps across three frameworks. Three were critical: missing access control documentation, no incident response plan, and an expired penetration test. Without a systematic scan, those gaps would have surfaced during the audit itself. Instead, Priya had a prioritized remediation plan before her second Monday.
What Muin for Compliance Does
The Compliance module addresses four core areas:
| Capability | What It Does | Key Features |
|---|---|---|
| Framework Management | Track requirements across SOC 2, ISO 27001, GDPR, HIPAA, PCI-DSS, NIST CSF, CCPA, and custom frameworks | Multi-framework mapping, update tracking, control cross-referencing |
| Gap Analysis | Identify where you stand against each framework | Prioritized gaps by severity, remediation steps, timeline recommendations |
| Risk Assessment | Maintain a living risk register with scoring and mitigation tracking | Likelihood/impact scoring, control mapping, automated review reminders |
| Audit Management | Organize evidence, track findings, and generate audit-ready reports | Evidence library, finding tracker, report generation, timeline views |
Framework Tracking
Every compliance framework is a set of requirements. Muin maps each requirement to your current status:
| Status | Meaning | Action Required |
|---|---|---|
| Compliant | Evidence attached, control verified | Maintain and refresh evidence |
| Partially Compliant | Some controls in place, gaps identified | Close gaps per remediation plan |
| Non-Compliant | Control missing or inadequate | Immediate attention needed |
| Not Applicable | Documented justification for exclusion | Ensure justification is current |
Supported Frameworks
| Framework | Focus Area | Typical Industries |
|---|---|---|
| SOC 2 | Security, Availability, Confidentiality | SaaS, Tech, Professional Services |
| ISO 27001 | Information Security Management | All industries (international) |
| GDPR | Data Protection & Privacy | Any company handling EU data |
| HIPAA | Protected Health Information | Healthcare, Health Tech |
| PCI-DSS | Cardholder Data | E-commerce, Payments, Retail |
| NIST CSF | Cybersecurity risk management | All industries |
| CCPA | Consumer privacy | Companies handling California resident data |
SOC 2 Type II and US Nonprofit Governance import from built-in templates with their controls ready to track. Other frameworks, and any custom framework of your own, are created on the Frameworks screen and mapped to the same controls. See the Frameworks docs.
Risk Register
The risk register is the center of your compliance posture. Each risk entry captures:
- Likelihood and impact scoring (quantitative or qualitative)
- Current controls in place
- Residual risk after controls
- Mitigation plan with owner and timeline
- Review schedule with automated reminders
AI assists by suggesting risk categories based on your industry and the frameworks you’re tracking. It won’t replace your judgment, but it ensures you’re not missing obvious risks.
Gap Analysis
Gap analysis compares your current state against framework requirements. The output is actionable:
- Prioritized list of gaps by severity and effort
- Suggested remediation steps
- Timeline recommendations based on audit dates
- Evidence collection checklists
Run gap analysis on demand or schedule it to refresh automatically as your compliance data changes.
Audit Preparation
When audit time comes, everything is already organized:
- Evidence library linked to specific controls and requirements
- Finding tracker for audit observations with response management
- Report generation with framework-specific formatting
- Timeline view of all compliance activities for the audit period
The AI can draft initial responses to audit findings based on your existing documentation and controls, saving hours of preparation time.
Compliance Score Engine
Most compliance management is binary: you’re either “compliant” or “not.” That’s not helpful when you’re trying to prioritize work or show progress to leadership.
Muin’s Compliance Score Engine provides a real-time 0-100 compliance posture score with per-framework breakdown:
- Per-framework scores: see your SOC 2 score separately from your GDPR score
- Control-level detail: drill into which specific controls are strong or weak
- Trend tracking: watch your score improve (or catch it slipping) over time
- Drift alerts: get notified when your compliance posture degrades below a threshold
The score updates automatically as you add evidence, close gaps, and complete remediation tasks. Leadership gets a number they can track. Your team gets a prioritized list of what to work on next.
Your audit readiness score updates in real-time. When the auditor calls, you will know exactly where you stand right now, without a frantic scramble to gather evidence and patch gaps. That confidence changes how you approach compliance: from a dreaded annual event to a continuous posture you maintain without thinking about it.
Security Questionnaire Pre-Fill
If you’ve spent hours filling out a security questionnaire from a prospect or partner, you know the pain. The questions are mostly the same across questionnaires, but the answers need to reference your specific policies and controls.
Muin’s Questionnaires screen gives you a head start:
- Add the questionnaire’s questions to Muin
- Pre-fill a draft answer for each question by matching it to a compliance category and citing the controls from your active frameworks
- Review and edit each draft, attach more sources, or write answers for questions that did not match
- Bulk approve the questions you are happy with
- Export the completed questionnaire
Each draft shows a confidence score and the controls it cites, so a reviewer can check it before anything goes out. Drafts are a starting point that a person finishes, not a finished answer. See the Security Questionnaires docs.
Evidence Freshness Alerts
Stale evidence is one of the most common audit findings. A screenshot from 18 months ago doesn’t prove your current posture.
Muin tracks evidence freshness automatically:
- Configurable thresholds: set how old evidence can be before it’s flagged (30, 60, 90 days)
- Automatic alerts: get notified when evidence approaches its expiration
- Auto-collection: for platform-generated evidence (audit logs, access controls, encryption status), Muin refreshes evidence automatically
- Evidence packages: generate auditor-ready evidence bundles with freshness timestamps
Because Muin also runs your HR, finance and documents, much of your evidence generates itself through normal usage. Audit logs, access controls, and encryption settings are always current because they’re always active.
Trust Center
Muin maintains a public Trust Center that provides transparency into our security posture, compliance frameworks, sub-processors, and data residency. Visit it to verify our security practices before trusting us with your data.
Your compliance data within Muin (frameworks, controls, evidence, and scores) gives you the raw material to answer security questions from prospects and partners quickly, especially when combined with questionnaire pre-fill.
Muin vs. Traditional Compliance Tools
| Feature | Spreadsheets | Standalone GRC | Muin for Compliance |
|---|---|---|---|
| Framework tracking | Manual | Yes | Yes + AI-assisted |
| Evidence collection | File folders | Upload-based | Auto-collected from platform |
| Risk scoring | Manual calculation | Yes | Yes + AI suggestions |
| Gap analysis | Point-in-time | Periodic | Continuous + real-time |
| Questionnaire filling | Hours each | Template-based | Template-based pre-fill citing your frameworks |
| Connected to business data | No | No | Yes: HR, Finance, Documents |
| Price range | Free (but costly in time) | Varies widely by vendor | One of your plan’s modules ($50/mo as an extra module) |
Who This Is For
Muin for Compliance is designed for businesses and nonprofits that need to demonstrate compliance, whether one person owns it or a dedicated team does. If you’re a startup preparing for SOC 2, a healthcare organization maintaining HIPAA, or a financial services firm tracking multiple frameworks, this module gives you the structure and automation to stay audit-ready without the overhead.
Getting Started
The Compliance module is available on every plan as one of your plan’s modules. Start by selecting the frameworks relevant to your business, and Muin will guide you through the initial assessment.
Start your free trial to get started.
Related Reading
- Why Privacy-First AI Matters for Your Business Data: Enterprise-grade privacy with AWS Bedrock
- Introducing Muin: the connected operations platform for businesses and nonprofits
- Muin for HR: Compliance, onboarding, and certification tracking
- Compliance Frameworks: Documentation for tracking SOC 2, ISO 27001, GDPR, HIPAA, and more